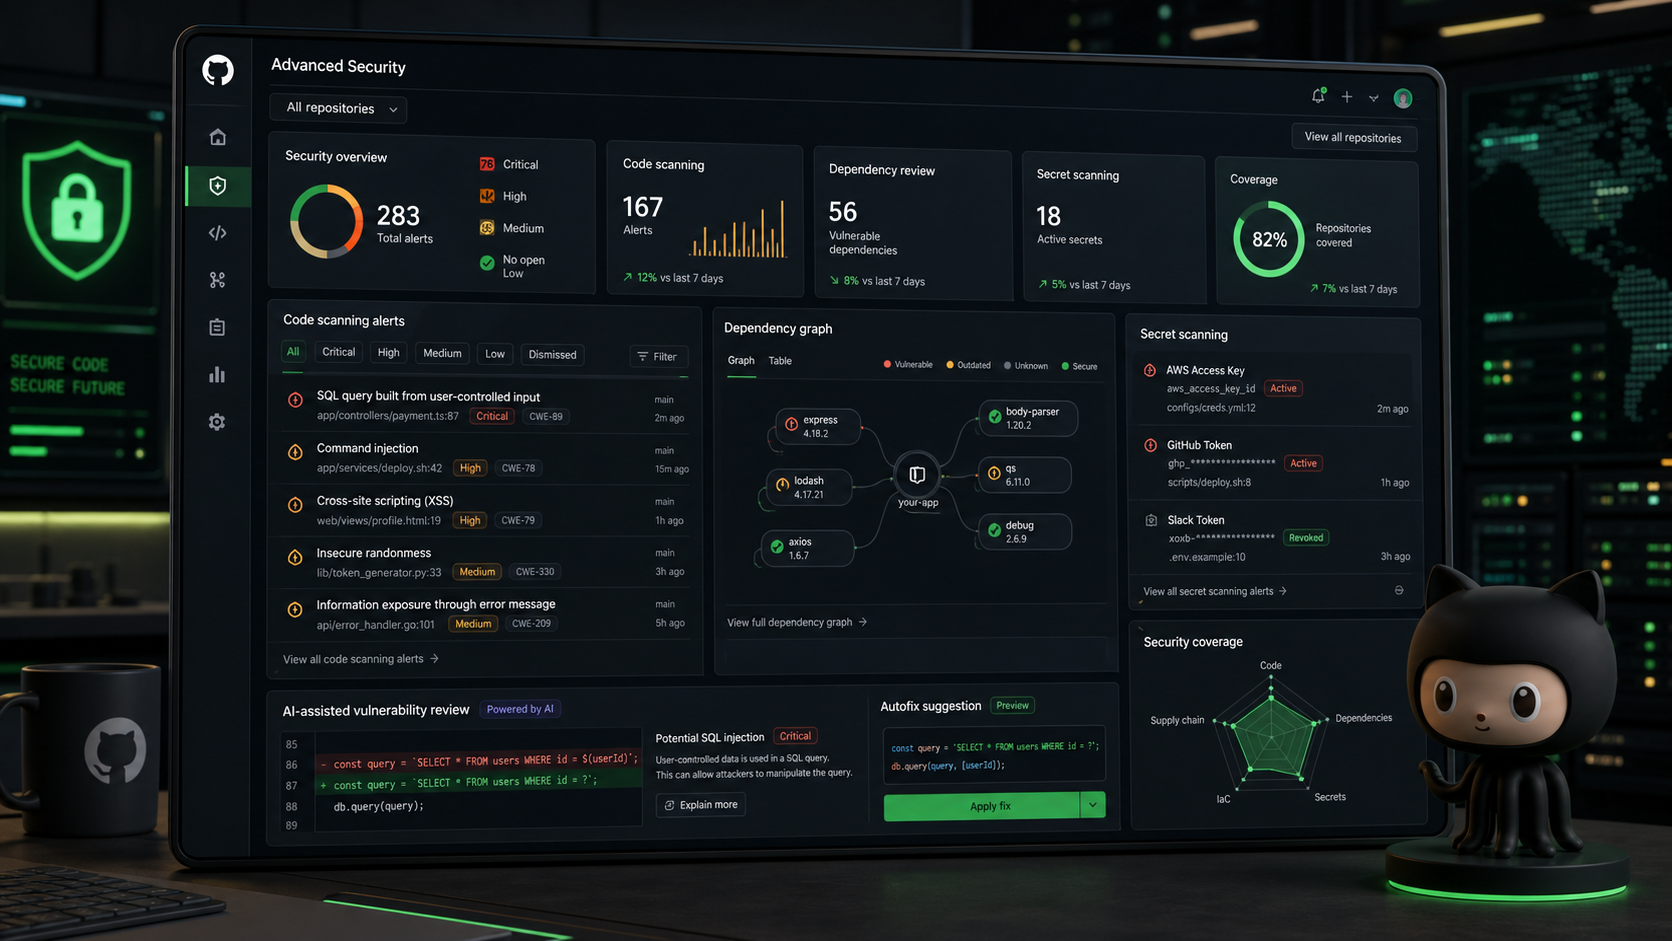
A Microsoft Security Blog article published on October 6, 2026, compiles CISO perspectives on managing vulnerability risks in the age of AI.
The piece presents security leaders’ viewpoints as organisations adopt increasingly AI-powered systems.
WHAT THE ARTICLE COVERS
The article collects insights from CISOs on how vulnerability risks are being managed in AI-enabled environments. TechStaged has also covered Microsoft Security Blog publishes threat matrix for cloud web applications.
It frames AI integration as a context in which risk management considerations become a priority for security leadership.
WHY THE PERSPECTIVES MATTER
As organisations scale AI usage, CISOs emphasize the importance of ongoing risk assessment and governance around vulnerabilities.
The compilation signals a shift in focus for security teams toward AI-related threat surfaces.
RELATED COVERAGE
- Microsoft Security Blog publishes threat matrix for cloud web applications
- Storm-3168: Agentic-driven cloud attacks hinge on compromised service principals, Microsoft Security Blog reports
- OpenAI's Defender’s Window foregrounds AI-driven shifts in cybersecurity
- Nvidia New AI Security Alliance Wants a Shared Incident Language
- Security articles
SOURCES
- Microsoft Security Blog: CISO perspectives on managing vulnerability risks in the age of AI Published · Primary source