From the Microsoft Security Blog, two verified statements are presented as facts:
QUOTED FACTS
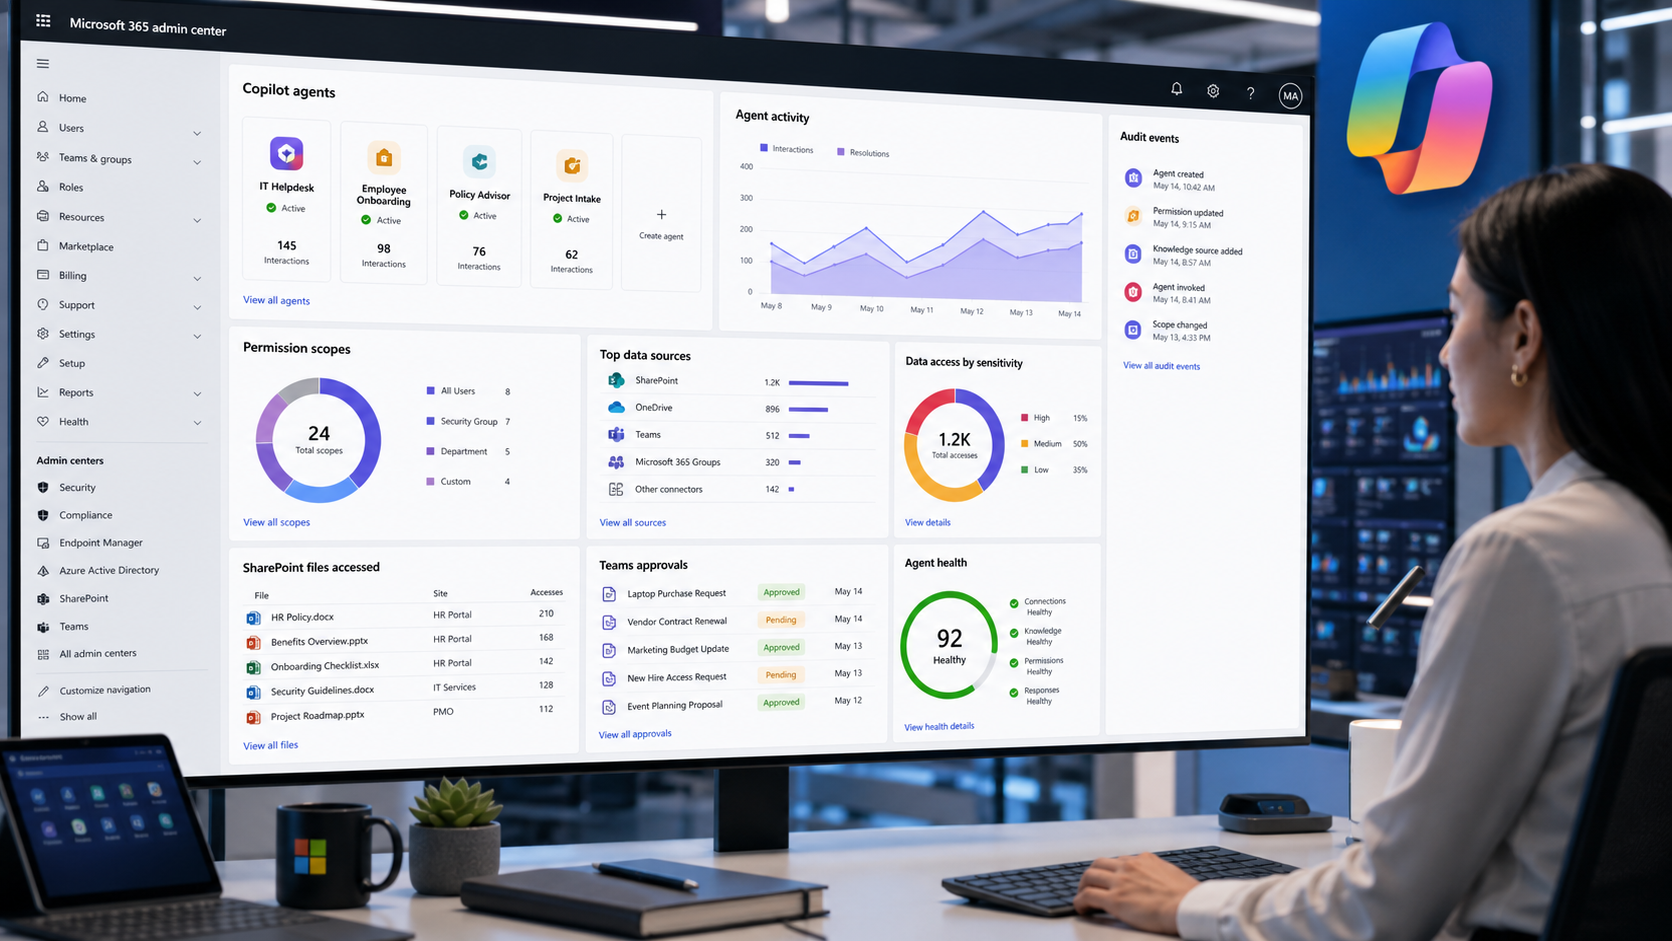
Agents are your newest insiders.
Security must move at their speed.
WHAT THESE FACTS IMPLY FOR SECURITY PRACTICE
Our analysis suggests that treating agents as insiders implies a need for security that can operate at the pace of agent-driven workflows.
This could require more automated telemetry and faster decision-making processes to align with agent actions.
LIMITATIONS OF THE EVIDENCE
The evidence in this piece comes from a single source in the supplied package (S1). There are no corroborating sources in the provided materials.
WHAT READERS CAN DO NOW
Based on the analysis, readers could consider the following plausible directions to align security with agent speed. These are not prescriptive requirements, but contextually reasonable steps given the evidence:
• Review IAM policies to enable rapid, yet principled, action for agent-authenticated activities while maintaining least privilege.
• Build telemetry that captures agent-level events and supports automated, rapid responses.
• Define a feedback loop between agent design and security monitoring to reduce latency in threat detection.
RELATED COVERAGE
- CISOs weigh vulnerability risk management in the AI era
- Microsoft Security Blog publishes threat matrix for cloud web applications
- Post-quantum authentication: Why organizations should start testing certificate ecosystems now
- Storm-3168: Agentic-driven cloud attacks hinge on compromised service principals, Microsoft Security Blog reports
- Security articles
SOURCES
- Microsoft Security Blog: Agents are your newest insiders. Security must move at their speed. Published · Primary source